Learn how EDR monitors endpoint behavior, identifies suspicious activity, supports investigation, and helps security teams respond when business devices show signs of compromise.
Managed EDR services help businesses monitor endpoint activity, detect suspicious behavior, investigate potential threats, and support faster response when computers or servers show signs of compromise.
Traditional antivirus remains useful for preventing many common threats. However, modern attacks may involve unusual processes, malicious scripts, stolen credentials, or legitimate system tools being used in unexpected ways.
Why Businesses Use Managed EDR Services
Business endpoints are where employees access email, cloud applications, files, customer information, and internal systems. For example, laptops and workstations process credentials, downloads, documents, and application data throughout the day.
As a result, endpoints are an important place to detect suspicious activity. Managed EDR services can provide deeper visibility into what a device is doing and help identify events that deserve investigation.
What Is Endpoint Detection and Response?
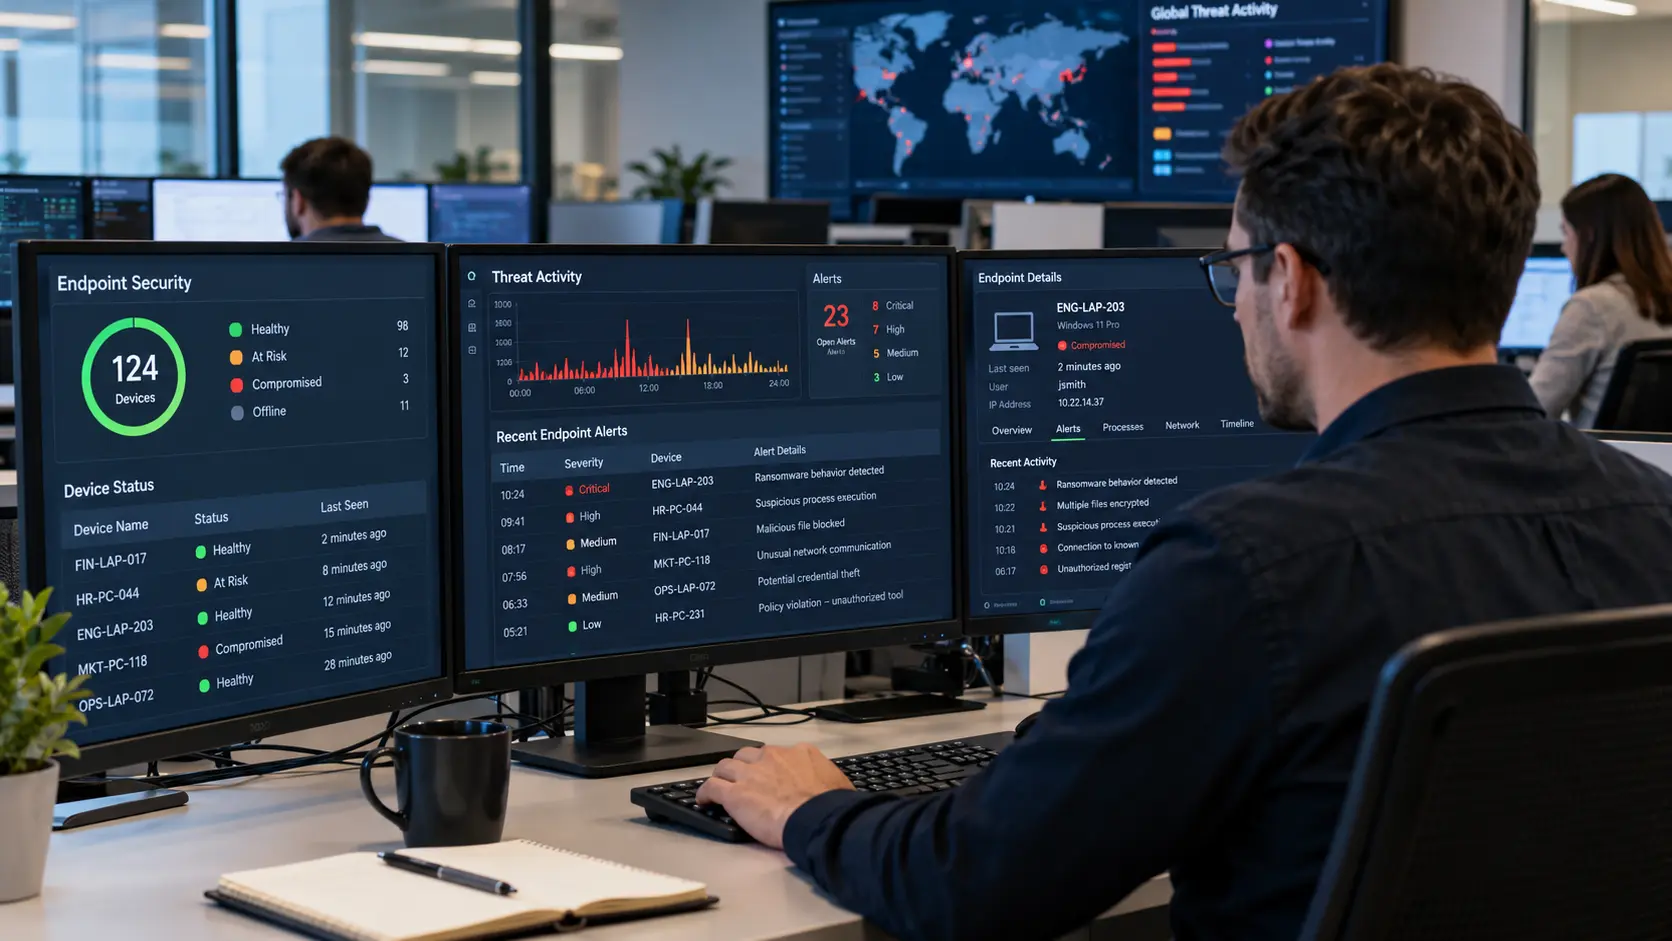
Endpoint Detection and Response, commonly shortened to EDR, is a security capability designed to monitor endpoint activity, identify potentially malicious behavior, provide investigation data, and support response actions.
Depending on the platform, EDR may collect information about processes, files, user activity, network connections, system changes, and other security-relevant endpoint events.
The Australian Cyber Security Centre's guidance on Endpoint Detection and Response explains that EDR can centrally record system behavior, support incident detection, assist investigations, block certain communications, and isolate compromised computers.
How Do Managed EDR Services Work?
Managed EDR services begin with endpoint monitoring and collection of security-relevant activity from protected computers and servers.
That information can then be analyzed for behavior that may indicate a threat. In practice, the process may include:
- Monitoring endpoint activity
- Collecting security telemetry
- Analyzing processes and behavior
- Generating alerts for suspicious events
- Correlating related activity
- Providing investigation data
- Supporting containment or response actions
- Recording events for later review
Therefore, EDR provides more than a simple malware alert. It can offer context about what happened before and after suspicious activity appeared.
What Can EDR Detect?
The exact detections depend on the EDR platform and configuration. However, behavioral monitoring can help identify many types of suspicious activity that deserve investigation.
Examples may include:
- Unusual process execution
- Suspicious scripting activity
- Unauthorized privilege changes
- Unexpected network connections
- Malicious or unusual file behavior
- Credential-related activity
- Persistence attempts
- Potential lateral movement
- Attempts to modify security controls
- Behavior associated with known attack techniques
MITRE ATT&CK's Behavior Prevention on Endpoint guidance describes endpoint defenses that analyze processes, files, API activity, and other events for patterns associated with malicious behavior.
Managed EDR Services vs. Traditional Antivirus
Antivirus and EDR overlap in some areas. However, they are not the same security control.
Traditional Antivirus
Antivirus typically focuses on identifying and blocking known malware and suspicious files. Modern antivirus may also include behavioral protections, web filtering, and other preventive security features.
Endpoint Detection and Response
EDR adds deeper endpoint visibility, investigation data, behavioral detection, alerting, and response capabilities. Therefore, security teams can investigate activity across the endpoint instead of focusing only on one suspicious file.
In many environments, antivirus and EDR work together as complementary layers of endpoint protection.
Why Behavioral Detection Matters
Attackers do not always rely on obviously malicious files. Instead, they may use legitimate administrative tools, scripts, built-in system utilities, or stolen credentials in unexpected ways.
For example, a system tool may be normal when used by an IT administrator but more concerning when it suddenly appears after a suspicious login or on a device where it is rarely used.
Because of this, behavioral detection focuses on what processes and users are doing rather than relying only on whether a file has already been identified as malware.
How EDR Helps Investigate Security Alerts
Detection is only the first step. Once suspicious activity appears, someone needs enough information to understand what happened and whether further action is necessary.
EDR investigation data may help answer questions such as:
- Which device generated the alert?
- What process started the suspicious activity?
- Which user account was involved?
- Did the activity create or modify files?
- Did the device communicate with unusual destinations?
- Were other endpoints involved?
- Did the activity attempt to change security settings?
- What happened immediately before and after the alert?
As a result, EDR can provide more context than an isolated warning that simply says a threat was detected.
How EDR Supports Threat Response
Depending on the platform and configuration, EDR can also support response actions after suspicious activity is identified.
For example, response capabilities may include:
- Isolating a compromised endpoint from the network
- Stopping a suspicious process
- Quarantining malicious files
- Blocking selected network communications
- Collecting additional investigation information
- Starting an incident-response workflow
CISA's Continuous Diagnostics and Mitigation technical capabilities describes EDR functions for centralized endpoint monitoring, alerting, management, and configured response actions.
However, automated response should be configured carefully because different business systems have different operational requirements.
Why Managed EDR Services Still Need Human Oversight
Managed EDR services can generate valuable alerts and support automated response actions. However, no security platform can understand every business event perfectly.
For instance, an unusual process may represent malicious activity, or it may be legitimate work performed by an administrator. Therefore, experienced review helps determine whether an alert requires investigation or can be safely closed.
This is especially useful for businesses without dedicated internal cybersecurity staff. The technology can identify activity, while trained professionals provide context, investigation, and response support.
Attackers May Try to Disable Endpoint Security
Attackers sometimes attempt to disable endpoint protections after gaining access to a system. As a result, monitoring the health and status of security tools is important.
In August 2026, BleepingComputer reported on an Akira ransomware intrusion in which an attacker reportedly used Safe Mode with Networking to interfere with endpoint security components after initial access. Read BleepingComputer's report on the attempted EDR bypass .
This does not mean EDR is ineffective. Instead, the incident shows why businesses should combine endpoint detection with strong authentication, vulnerability management, secure remote access, monitoring, backups, and other security controls.
What Do Managed EDR Services Include?
Managed EDR services combine endpoint detection technology with ongoing monitoring, alert review, investigation, and response support.
As a result, businesses do not have to rely only on individual employees to notice or interpret security warnings.
Depending on the service, managed EDR may include:
- EDR deployment and configuration
- Endpoint monitoring
- Alert review
- Threat investigation
- Incident escalation
- Device isolation or containment support
- Security reporting
- Coordination with patching and vulnerability management
Consequently, the value comes not only from installing endpoint detection technology but also from maintaining and responding to the information it generates.
How SecuraLynx Supports EDR Through Endpoint Security
SecuraLynx includes Endpoint Detection & Response as part of its broader managed endpoint security services .
The service also includes endpoint management, anti-malware, intrusion detection and prevention, patch management, device vulnerability checks, integrity checks, data protection, monitoring, alerts, and incident support.
Therefore, EDR is positioned as one layer within a broader endpoint-security strategy rather than as an isolated product.
How EDR Works With Patch and Vulnerability Management
EDR helps detect suspicious endpoint activity, while patch management aims to reduce vulnerabilities that attackers may try to exploit.
For this reason, businesses should combine threat detection with regular security updates and vulnerability management rather than relying on EDR to compensate for outdated software.
SecuraLynx includes patch and update management along with device vulnerability checks within its endpoint-security service. As a result, preventive controls and detection capabilities can support one another.
How Security Monitoring Supports Managed EDR Services
Endpoint alerts become more useful when someone consistently reviews, prioritizes, and investigates them.
SecuraLynx's managed security monitoring services provide broader visibility into alerts, endpoint activity, networks, accounts, vulnerabilities, and other security events.
In addition, combining EDR with ongoing monitoring can help businesses maintain more consistent oversight as devices, employees, and systems change.
How a Cybersecurity Risk Assessment Can Identify Endpoint Gaps
Businesses may have endpoint security installed without knowing whether every important device is covered or whether other security gaps remain.
For example, older devices, remote systems, missing patches, unsupported software, or weak configurations may increase exposure even when EDR is present.
A cybersecurity risk assessment can help review devices, accounts, vulnerabilities, configurations, monitoring, backups, and other controls.
As a result, EDR can be evaluated as one part of the overall cybersecurity environment instead of being expected to solve every endpoint-security problem on its own.
Does EDR Stop Every Cyberattack?
No. Endpoint Detection and Response can improve threat visibility, investigation, and response. However, no EDR platform can guarantee complete protection from every attack.
Attackers may target credentials, cloud accounts, networks, employees, remote access, unpatched software, or other areas outside a single endpoint-security tool.
Therefore, businesses should use EDR as part of a layered security strategy that also includes strong authentication, patch management, network security, backups, monitoring, and employee awareness.
What Should Businesses Look for in Managed EDR Services?
Businesses comparing managed EDR services should look beyond whether endpoint detection software is installed.
Useful questions include:
- Which endpoint types are supported?
- Who reviews EDR alerts?
- How are important threats investigated?
- What response actions are available?
- How are false positives handled?
- Does the service include vulnerability management?
- Are patches and security updates monitored?
- How are remote devices protected?
- Are incidents documented and reported?
- Who provides support during a serious incident?
Ultimately, businesses should understand both the endpoint technology and the team responsible for managing it.
Frequently Asked Questions
What does EDR stand for?
EDR stands for Endpoint Detection and Response. It refers to technology that monitors endpoint activity, identifies suspicious behavior, supports investigation, and provides response capabilities.
What is the difference between EDR and antivirus?
Antivirus primarily focuses on identifying and blocking malware. In contrast, EDR adds deeper endpoint monitoring, behavioral analysis, investigation data, alerting, and response capabilities.
Can EDR detect ransomware?
EDR may detect behaviors associated with ransomware and other threats, depending on the platform and attack. However, no endpoint-security technology can guarantee detection or prevention of every ransomware incident.
Can EDR isolate an infected computer?
Many EDR platforms support endpoint isolation or other containment actions. However, the available response capabilities depend on the technology, configuration, and managed service.
Do businesses still need antivirus if they use EDR?
In many environments, antivirus and EDR work together. Antivirus provides preventive malware protection, while EDR adds deeper detection, investigation, and response capabilities.
What are managed EDR services?
Managed EDR services combine endpoint detection technology with professional monitoring, alert review, threat investigation, response support, and ongoing endpoint-security management.
Make Managed EDR Services Part of Your Endpoint Security Strategy
Managed EDR services give businesses greater visibility into suspicious activity across laptops, workstations, and servers.
In addition, professional monitoring can help turn endpoint alerts into practical investigation and response instead of leaving important security notifications unattended.
However, EDR works best as one part of a broader cybersecurity strategy. Patch management, vulnerability checks, strong authentication, backups, network security, and ongoing monitoring remain important as well.
Who Is Watching Your Endpoint Security Alerts?
SecuraLynx can help review your endpoint-security environment, EDR coverage, vulnerabilities, patching, monitoring, and other controls that protect business devices.
From there, a cybersecurity assessment can help identify potential gaps and determine which managed endpoint-security services fit your environment.
Request an Endpoint Security Assessment